MetaMask reported a security incident affecting its Ethereum validator infrastructure on September 30, 2026, leading to the diversion of approximately 0.36 ETH in staking rewards. As a precaution, around 17,000 validators holding approximately 523,000 ETH are exiting, a process expected to complete by October 7, 2026. MetaMask confirmed no user wallets or funds were compromised.
The personal X account of Nano Labs founder Jack Kong was compromised and used to promote a fake AI trading token. Nano Labs confirmed the posts were unauthorized and warned users against engaging with the token.
A coordinated exploit targeting Fetch.ai, SingularityNET, and NuNet on September 19, 2026, resulted in approximately $17 million in unrealized gains for an attacker who compromised privileged signing keys. The attacker drained existing tokens and minted billions of new ones, causing token prices to collapse. All three projects have paused operations and deactivated vulnerable keys.
Bitcoin Lightning wallet Blink Wallet has paused services due to a security incident where an attacker accessed a limited number of custodial accounts and withdrew funds. Non-custodial wallets were unaffected, and the majority of funds remain secure. An investigation into the vulnerability is ongoing.
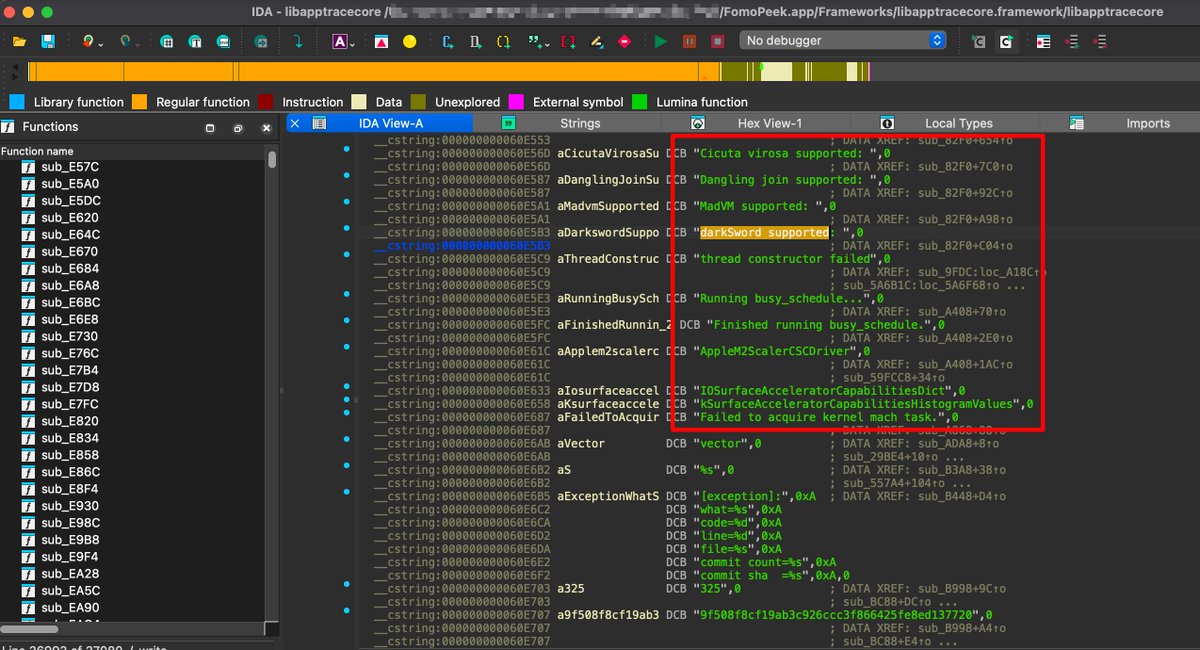
SlowMist reported that users of the FomoPeek App (versions 1.1-1.2) have had assets stolen due to private key exposure. Some affected users had previously installed and used the FomoPeek application.
DCENT issued an urgent security alert on September 16, 2026, reporting abnormal asset transfers detected in its mobile App Wallet. The issue appears limited to the App Wallet, with no confirmed impact on hardware wallets. Users are advised to transfer funds to secure hardware wallets.
WealthManagementV2 experienced a loss of 26,414 USDT. The root cause is suspected to be the illegal transfer of owner privileges, likely due to a leaked private key, allowing the attacker to set plans.
On September 3, 2026, approximately 4,011 XRPH Wallet user accounts were compromised due to seed phrase leakage, resulting in the theft of XRPH, XRPHAI, and other assets totaling around $452,000. The stolen funds were bridged to Ethereum and converted to DAI, which remains in a single address. The XRPH Wallet project confirmed the XRP Ledger itself was not affected, took the app offline, and is investigating.
A report indicates that a two-key breach could grant hackers control over $91 billion in USDT. The specific mechanism and current status of this potential threat are not detailed in the provided text.
Solana-based AMM Aquifer was exploited for approximately $2.5 million, with evidence suggesting compromised admin credentials or linked wallets rather than a smart contract bug. The attacker used addresses on both Solana and Ethereum. Aquifer's upgrade authority has offered a bounty for the return of at least 80% of the stolen assets by September 3, 2026.
Realio Network has halted webapp access following a security breach that resulted in the draining of 124 million RIO tokens. The incident highlights potential vulnerabilities in hybrid custodial platforms.
In May, one of StablR's three signing keys was compromised, allowing an attacker to mint tokens directly into their wallet. This incident occurred despite StablR being a licensed and compliant stablecoin issuer, with no custody breach or stolen funds involved.
The KITE Foundation detected compromised wallet addresses and paused ERC-20 transfers and cross-chain channels. A new contract was deployed, airdropping new tokens to legitimate addresses, with no asset losses reported.