MemTensor's AI memory tooling, including the MemoryOS library (PyPI) and the memtensor/memos-cloud-openclaw-plugin (npm), has been compromised
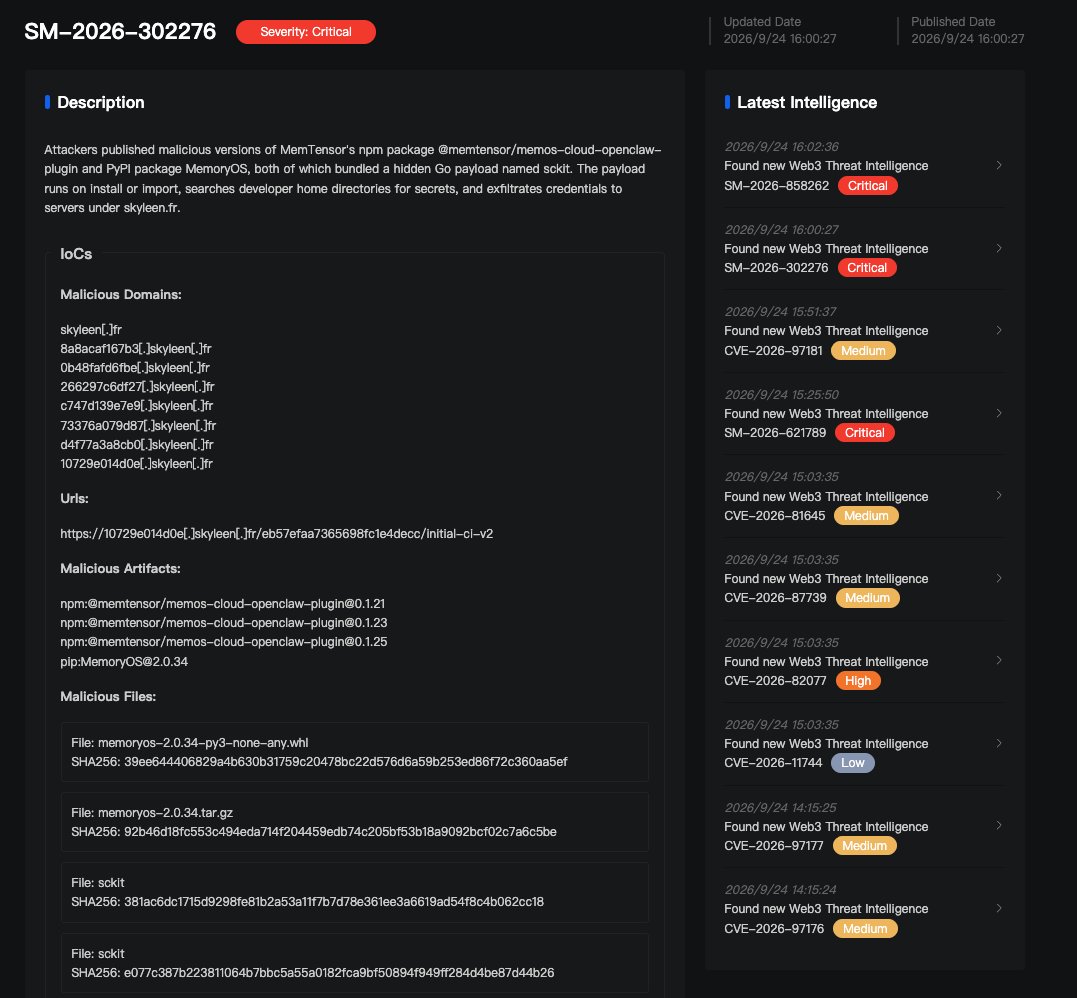
MemTensor's AI memory tooling, including the MemoryOS library (PyPI) and the memtensor/memos-cloud-openclaw-plugin (npm), has been compromised. This affects their open-source long-term memory library for LLM and AI agents and its official plugin for the OpenClaw agent.
- Protocols
- MemoryOS, memos-cloud-openclaw-plugin
- Confidence
- High
- First seen
- 24 Sep 2026, 10:08 UTC